256GRID · EU-HOSTED COMPUTE

Enterprise compute,
attested from silicon up.

Distributed HPC where every node proves itself in hardware before it joins. TPM 2.0 attestation, mutual-TLS zero-trust transport and a hash-chained audit log — built in the EU, auditable end to end.

Operating posture EU-hosted infrastructure Hardware-rooted trust Zero external dependencies ADR-first, honesty-disciplined
TPM 2.0 Per-node attestation

Every node runs a measured-boot quote check before it joins. An unattested node never receives work.

mTLS Zero-trust transport

Mutual-TLS 1.3 on every link, both directions. No bearer tokens in the data path.

EU Hosting & residency

European-resident infrastructure and operations by default — no dependency on non-EU clouds.

Hash-chained Tamper-evident audit

Every job is recorded in a hash-chained log with FROST-signed checkpoints — verifiable after the fact.

How it works

Trust that starts in the hardware.

256grid is a coordinator and a fleet of edge agents. A job is split, placed on attested nodes, run under confidential-compute isolation where the silicon supports it, and signed into a tamper-evident receipt. Only what is genuinely live is shown here.

Attested enrolment

Live

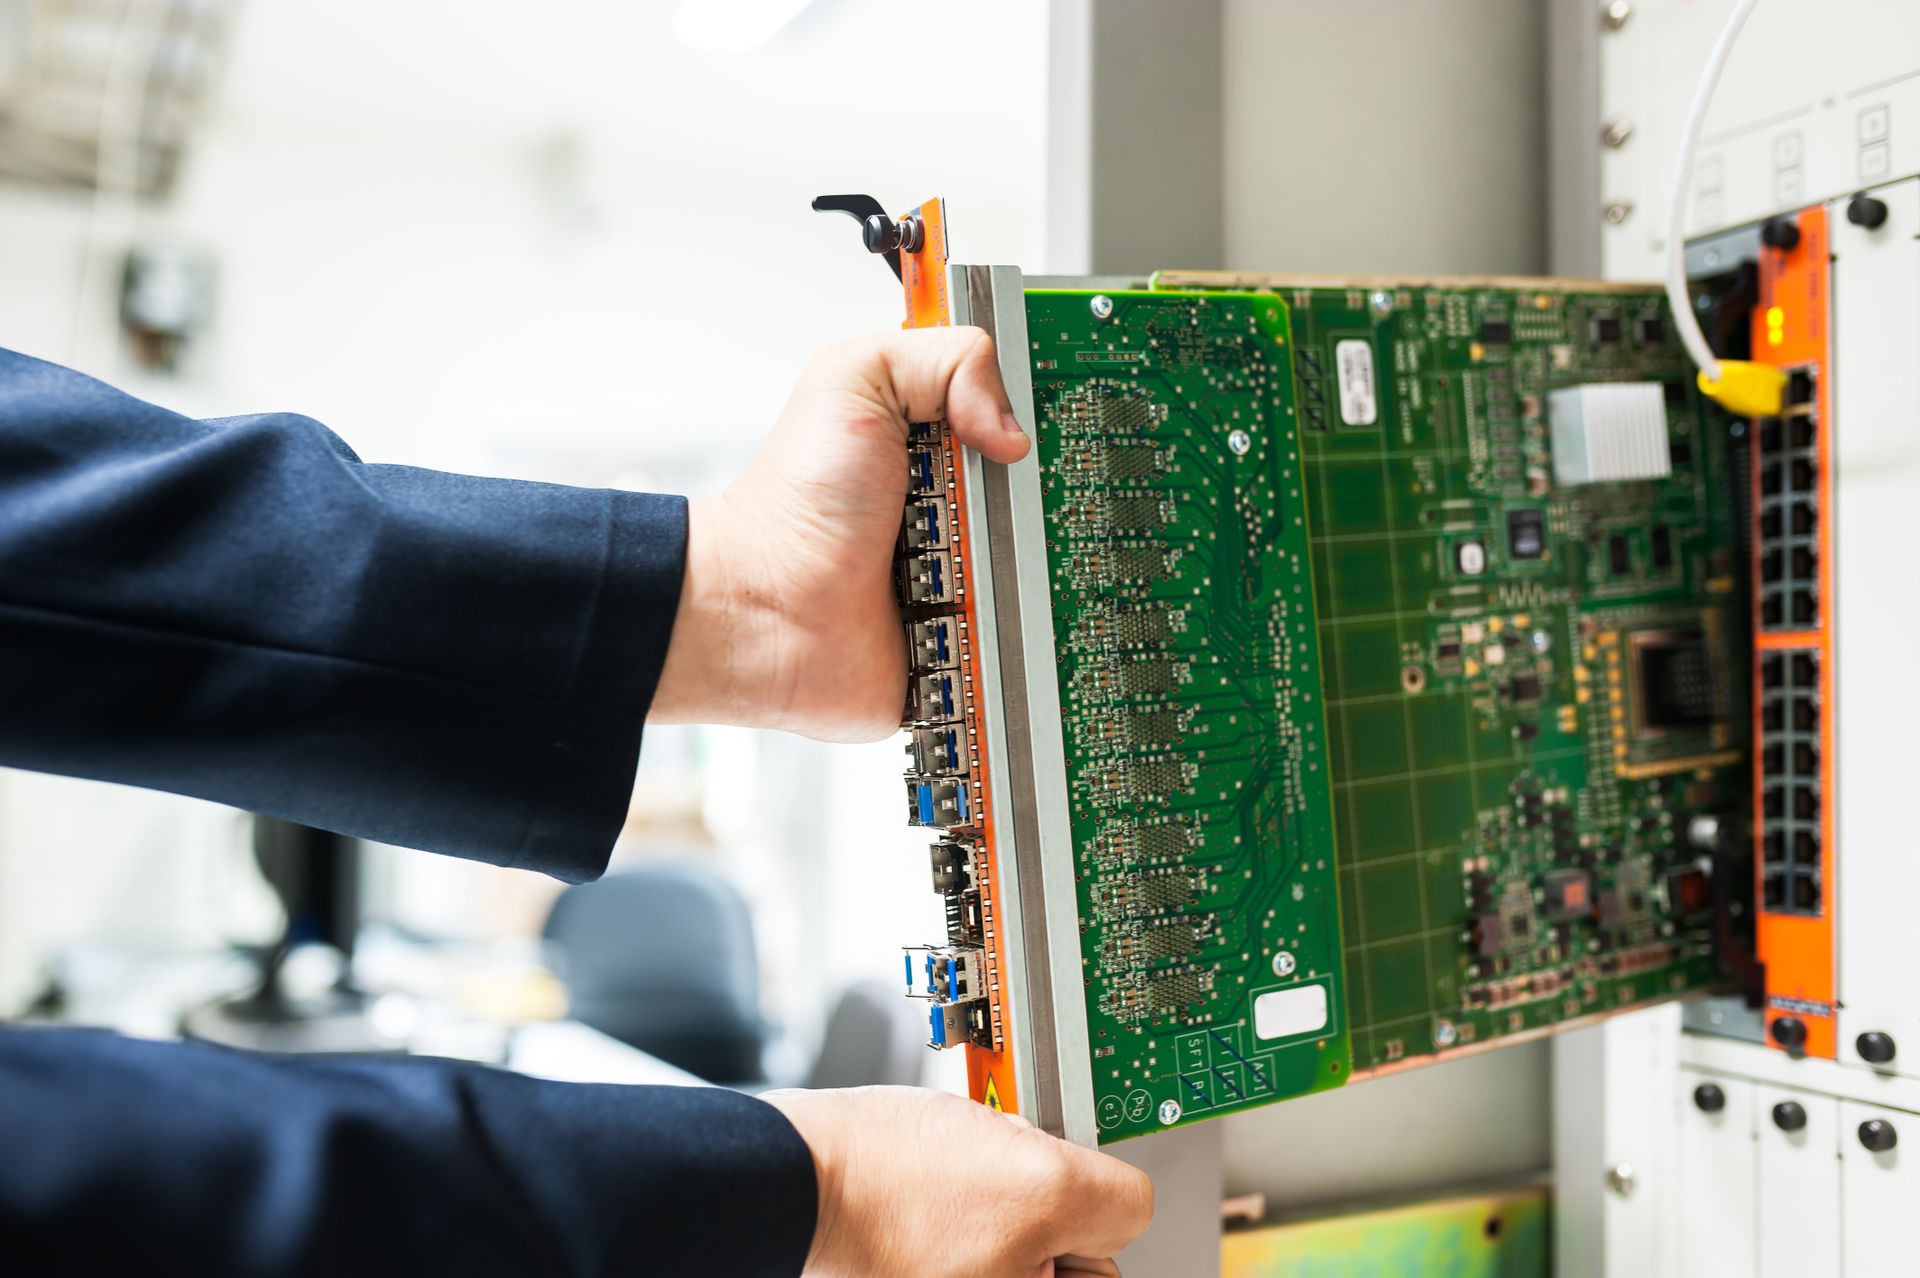
Nodes present a TPM 2.0 quote at enrolment; the coordinator verifies it against the attestation identity key before the node can take work. LUKS2 full-disk encryption is sealed to the boot measurements — tamper the boot chain and the node cannot start.

Hardware-rooted·Real

Sharded dispatch

Live

The coordinator splits a workload across the attested fleet, bin-packs it onto capacity, and aggregates the result. Each shard runs on a node that has proven itself; failures surface as job failures, never silent partial success.

Coordinator + agents·Real

Signed receipts

Live

Every job lands in a hash-chained audit log with FROST threshold-signed checkpoints, so a result can be verified independently long after it ran. Confidential-stream output never leaks plaintext back through the control plane.

Tamper-evident·Real
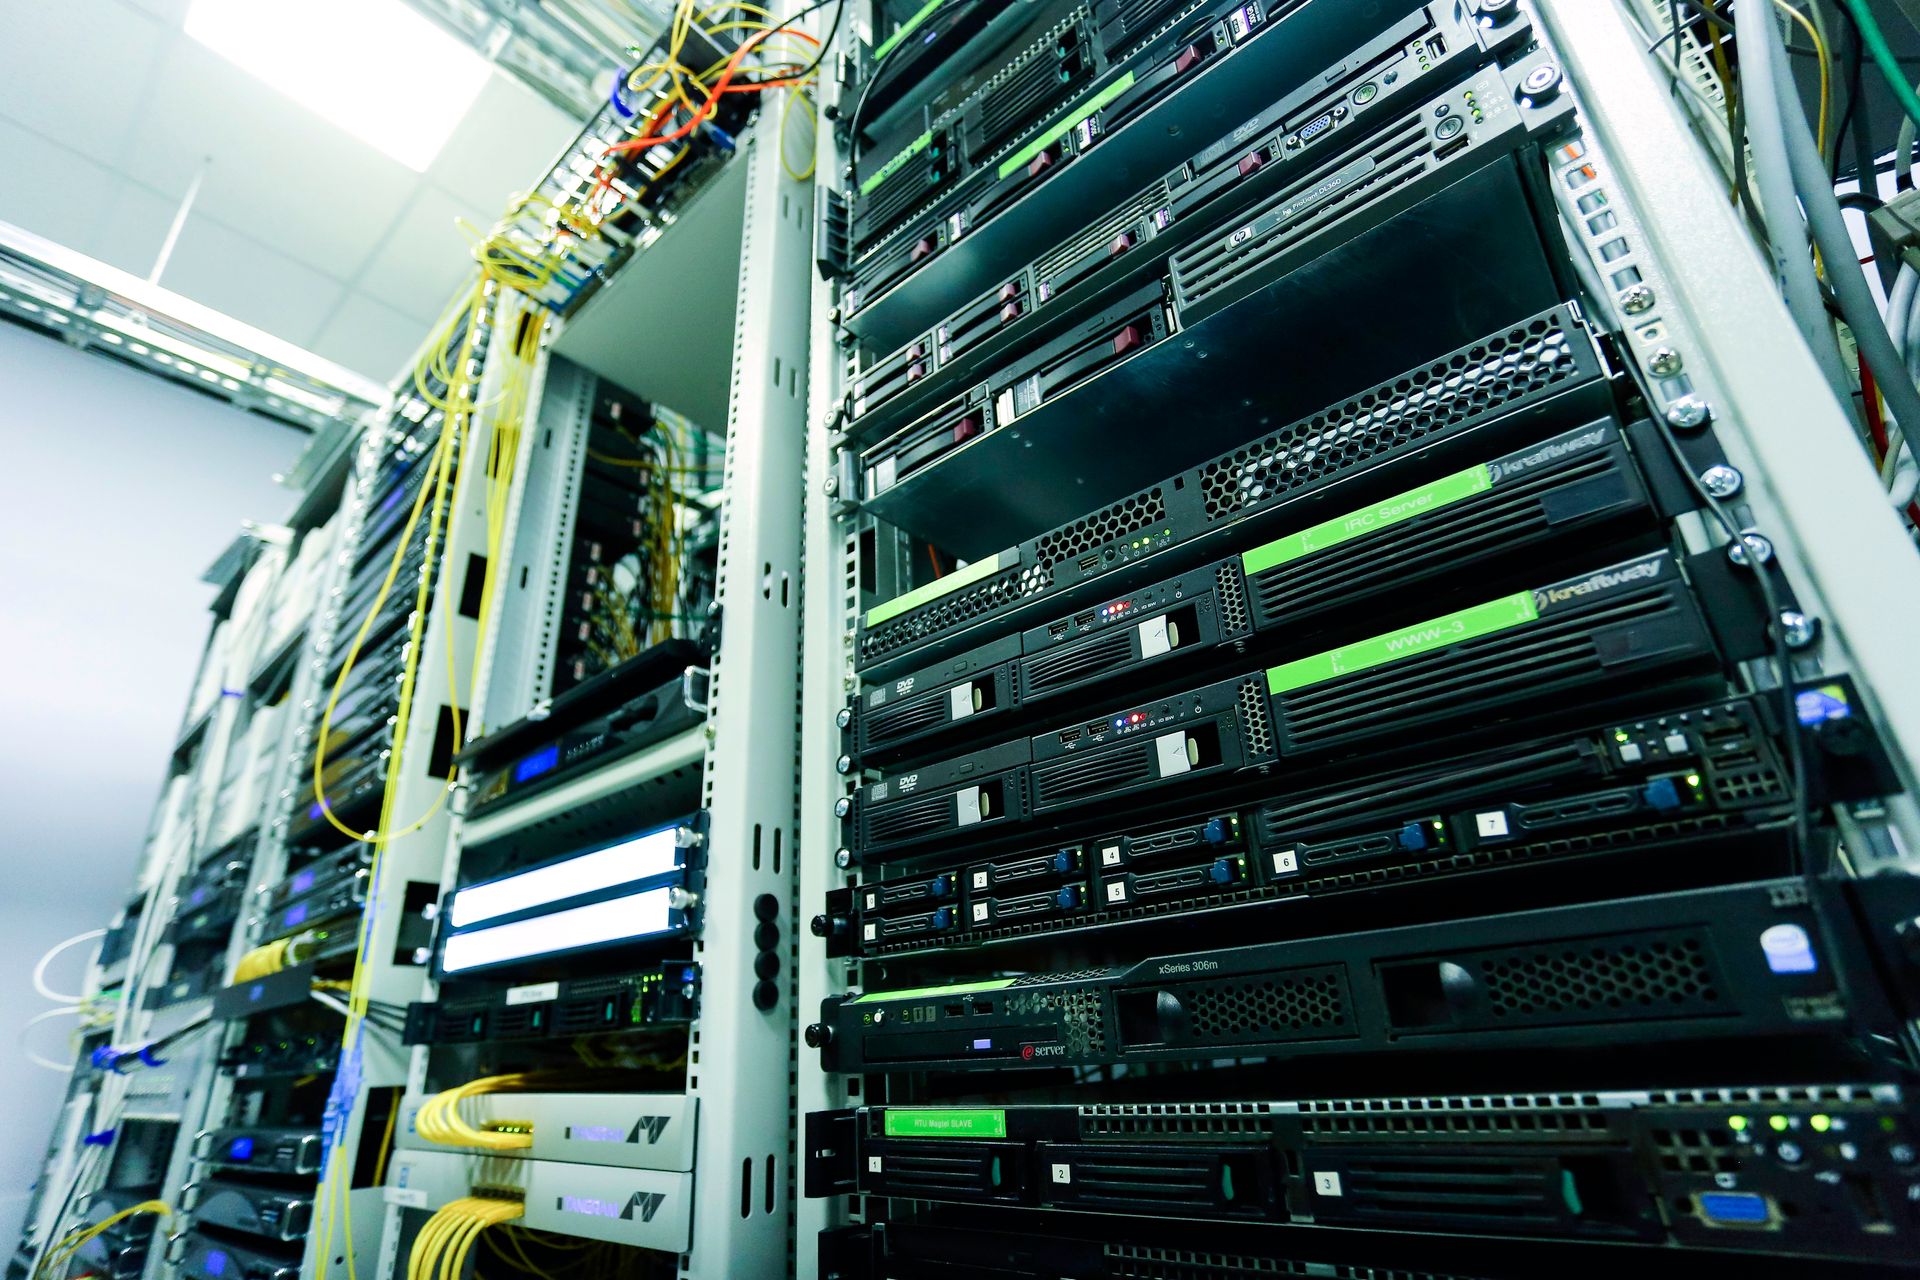
A row of server racks in a European datacenter

Real infrastructure

Our own silicon, in European datacenters.

256grid runs on real hardware we control — not a reseller's console. Every node is measured, attested and sealed before it joins the fleet, so the people who run workloads here can verify what ran, where, and that nothing else could read it.

How we build

Real, or not shown.

256grid is built with a brutal honesty discipline. Every capability is tagged REAL or MOCK; the public face shows only what actually runs. Hardware-attested confidential compute waits on the silicon that supports it — we will not claim it before it is real.

Talk to the team

Real, not mock.

Every feature is tagged REAL or MOCK. The platform refuses to ship work that blurs the line, and the public site shows only live capability.

Attested, not asserted.

Trust comes from a hardware quote the coordinator checks — not from a claim. Unverified nodes never join.

Auditable end to end.

Hash-chained logs and threshold-signed checkpoints mean a customer can verify what ran, after the fact, without trusting us.

EU-sovereign.

European-resident infrastructure, zero external front-end dependencies, no non-EU cloud in the trust path.

Get in touch

Request access to 256grid.

Enterprise and research compute, by introduction. Tell us what you need to run.

Request access